Elev8ai
From AI opportunity to responsible adoption.
Organisations aren't short of AI ideas.
The challenge is deciding which opportunities should proceed, under what conditions and with whose accountability.
Elev8ai helps organisations create a consistent pathway from an AI opportunity through assessment, impact and risk evaluation, decision, controls, registration and ongoing oversight.
Rather than treating AI governance as a compliance exercise, Elev8ai brings business, technology, security, privacy, risk and compliance into a common decision-making process.
How do we confidently say yes?
Elev8ai helps organisations establish:
what opportunity is being proposed and the value expected;
who owns and is accountable for it;
what data, systems and stakeholders are involved;
what risks, impacts and obligations need consideration;
what assessments and evidence are required;
whether the initiative should proceed and under what conditions; and
how approved AI is monitored throughout its lifecycle.
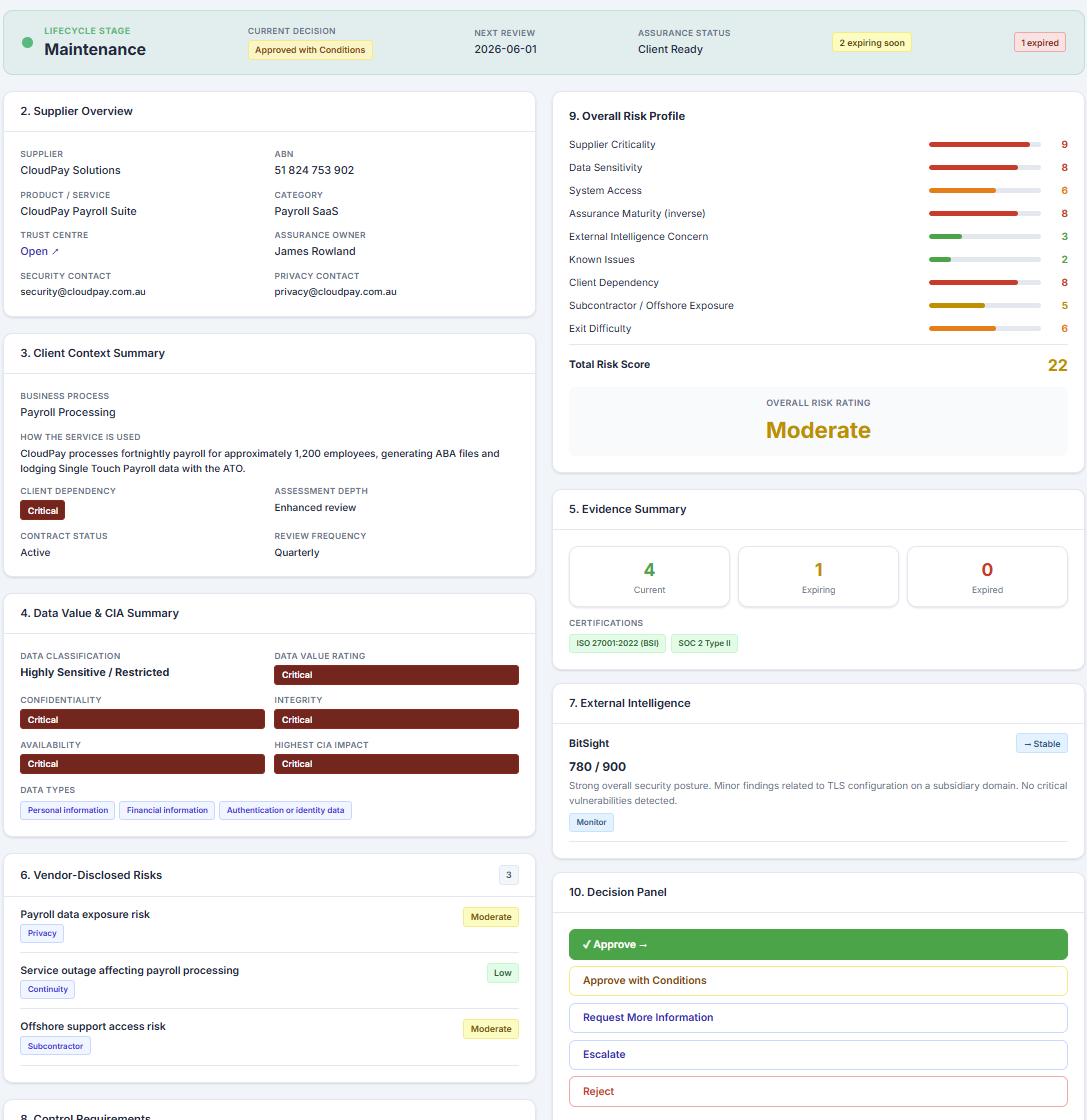
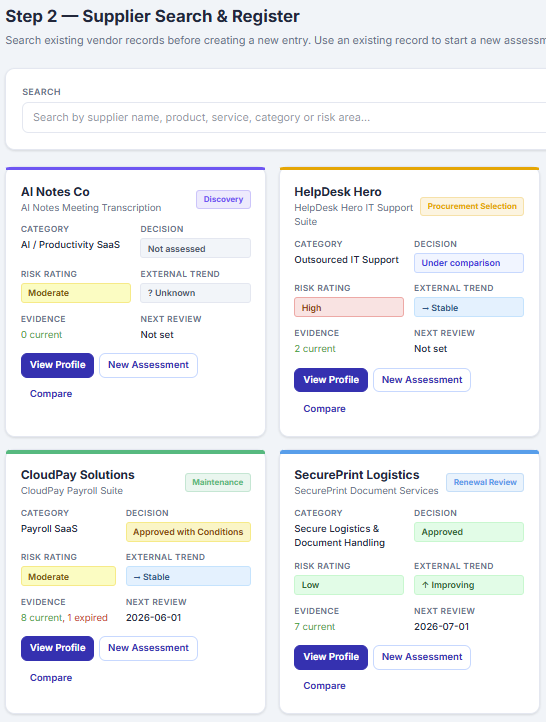
Shared Supplier Assurance Portal (SSAP)
Not just supplier questionnaires. Shared assurance in motion.
Traditional supplier risk tools often ask, “Has the questionnaire been completed?”
The Shared Supplier Assurance Portal asks:
What do we actually know about this supplier, what assurance already exists, and what still needs to be reviewed?
Because supplier assurance should not be a repeated paperwork exercise. It should help both parties understand risk, reduce duplication and make better decisions.
Suppliers: build your assurance profile once, maintain it over time
Clients: Make supplier assurance more consistent, risk-based and easier to oversee
The Shared Supplier Assurance Portal helps clients manage supplier assurance in a more structured and practical way.
Rather than relying on scattered spreadsheets, email trails and one-off questionnaires, clients can use SSAP to assess suppliers based on service criticality, risk exposure, assurance evidence, responsibilities and ongoing review requirements.
The portal is designed to help organisations understand supplier risk more clearly, reduce duplicated effort and make better-informed decisions before onboarding, renewing or continuing supplier relationships.
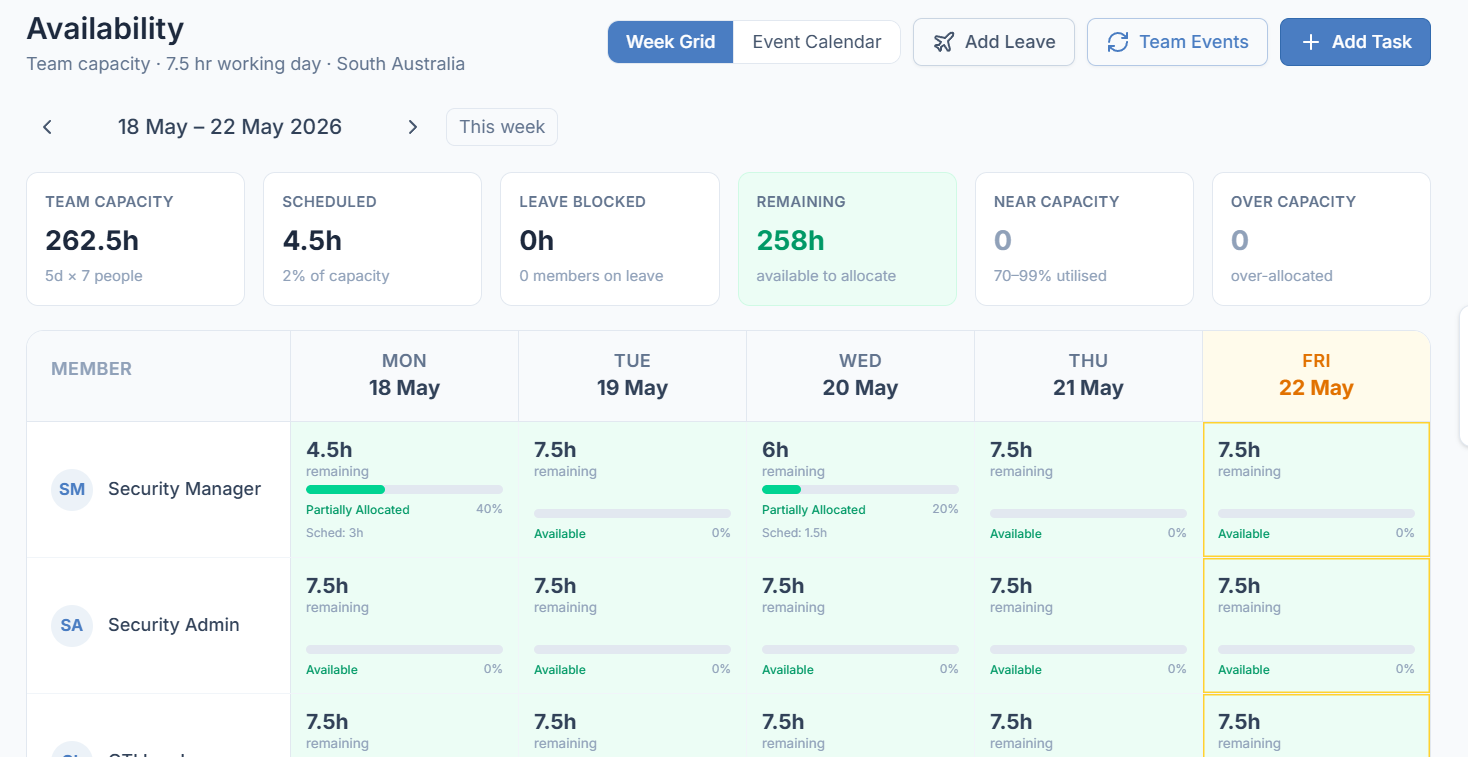
ISMS Cadence
Not just GRC. Governance in motion.
The ISMS Cadence Hub is built for the work that happens between audits — the activities, decisions, reviews, risks, controls and improvements that keep an ISMS alive.
Traditional GRC tools focus on storing compliance records. The Cadence Hub focuses on helping teams operate, manage and improve the ISMS throughout the year.
Because ISO 27001 should not be something you dust off before an audit. It should be part of how the organisation works.
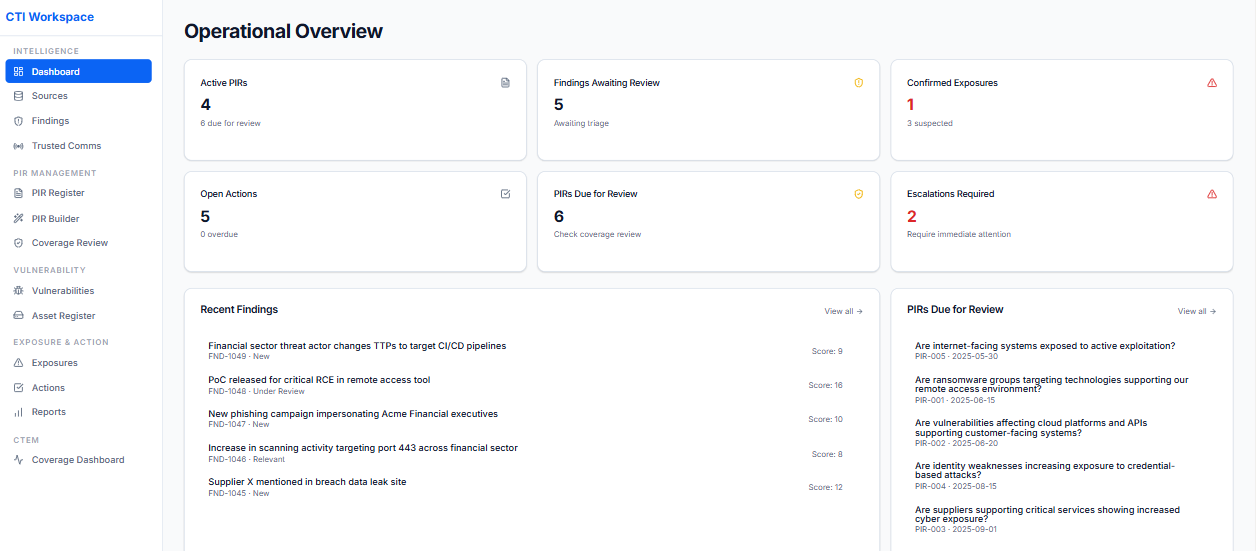
Cyber Threat Intelligence (CTI) Governance Platform
Not just threat feeds. Intelligence in motion.
Most threat intelligence tools focus on collecting more feeds, indicators, alerts and technical data.
The CTI Platform is built around a different question: what intelligence does the organisation actually need to make better decisions?
It helps teams define Priority Intelligence Requirements (PIRs), connect intelligence to assets, business processes, risks and exposures, and turn findings into actions and reports that matter to security leaders, executives and boards.
Traditional CTI tools often ask, “What threats are out there?”
The CTI Platform asks:
“Which threats matter to us, why do they matter, and what should we do about them?”
Because cyber threat intelligence should not create more noise. It should create focus.